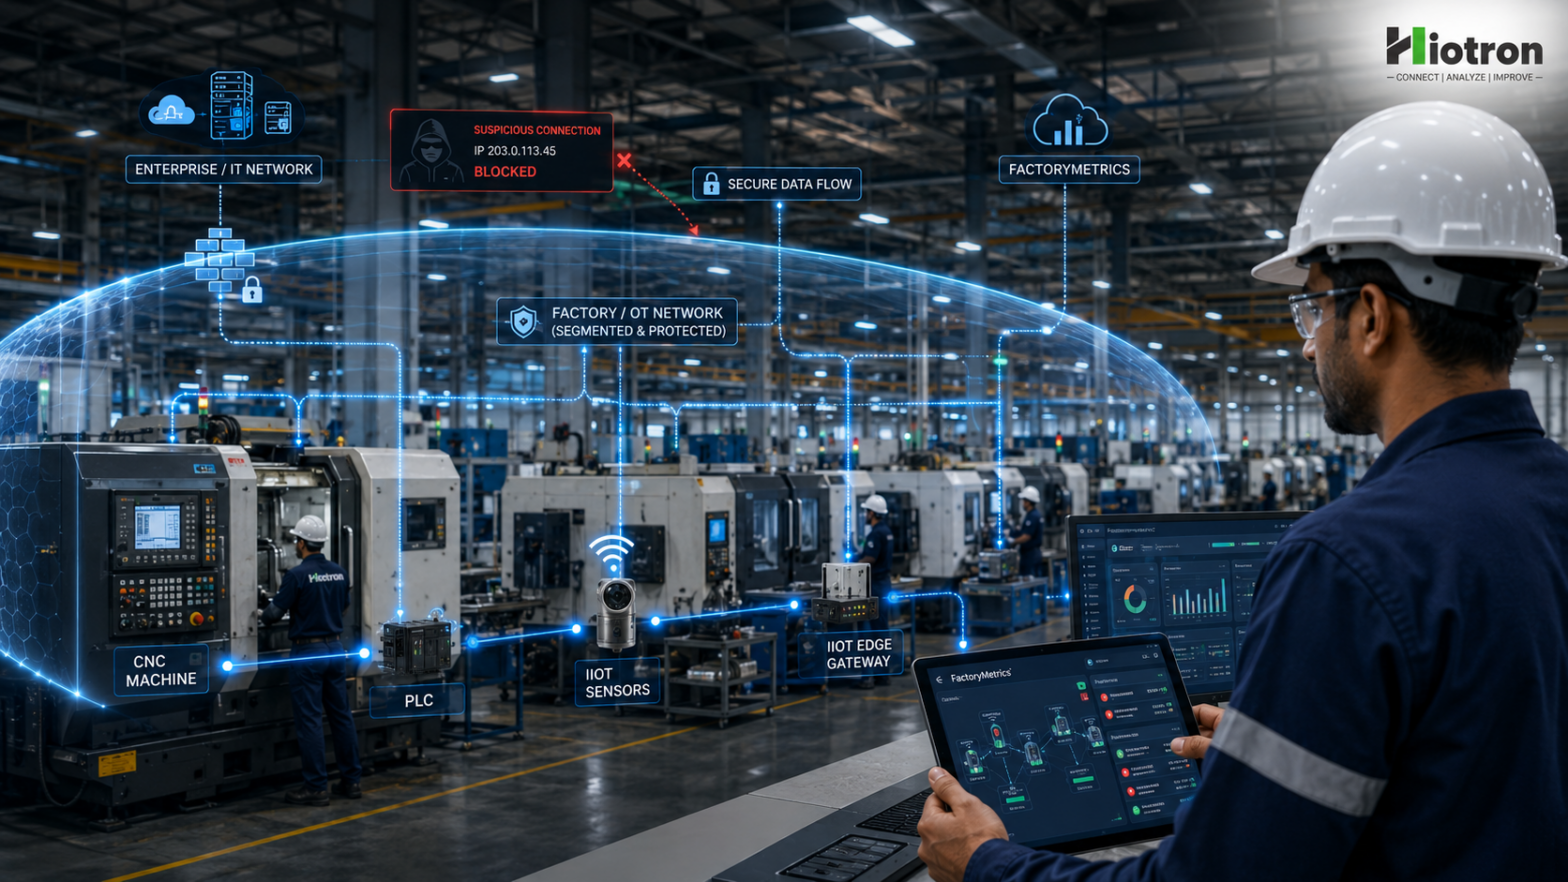
Manufacturing has become the most targeted sector for ransomware in India, and the reason is simple: factories are connecting thousands of sensors, PLCs, and SCADA systems to the internet faster than they are securing them. Industrial IoT security India is no longer a back-office IT concern — it is a production continuity issue that can halt an entire plant floor. According to the India Ransomware Report, manufacturing has overtaken IT and financial services as the most attacked industry, and globally, 75% of manufacturing ransomware cases disrupted operations to some degree. For plant managers and CTOs rolling out connected machines, sensors, and edge gateways, understanding how to secure this new attack surface is now a board-level priority, not just an engineering checklist.
Why Industrial IoT Security in India Has Become Urgent
India’s factories are digitizing at a pace that has outrun their security budgets. The country’s Operational Technology (OT) security market is valued at approximately USD 877.9 million in 2026 and is projected to grow at a CAGR of 19.4% to reach over $2.1 billion by 2031, driven by rapid industrialization, Make in India initiatives, and rising cyberattacks on critical infrastructure. That growth is a direct response to a threat landscape that is intensifying every quarter.
Globally, 80 ransomware groups targeted industrial organizations in 2024 — a 60% jump from 2023 — and manufacturing alone accounts for roughly 96,000 internet-exposed OT devices carrying known exploited vulnerabilities. In India specifically, plants running legacy PLCs alongside new IIoT sensors create a hybrid environment where old machines were never designed to resist modern network-based attacks.
The Cost of Ignoring OT Security
Roughly a third of manufacturing breaches worldwide now involve ransomware or extortion, and a quarter of those incidents force a complete shutdown of OT operations. For an Indian automotive or electronics plant running on thin margins and just-in-time production schedules, even a single day of downtime can cascade into missed shipments, contractual penalties, and reputational damage with global OEM customers.
Common Vulnerabilities in Indian Manufacturing IIoT Deployments
Before fixing IIoT cybersecurity manufacturing gaps, it helps to understand where they actually originate. Most incidents do not start with sophisticated nation-state exploits — they start with everyday operational shortcuts.
- Flat networks: IT and OT systems sharing the same network segment, letting an attacker who breaches an office laptop move laterally straight into the production line.
- Unmanaged devices: Sensors, gateways, and edge controllers added to the shop floor without being logged in a central asset inventory.
- Removable media and contractor access: USB drives and third-party laptops account for roughly 27% of OT security incidents, a especially common risk during vendor maintenance visits.
- Weak authentication: Many IIoT sensors and legacy PLCs ship with default credentials that are rarely changed after commissioning.
- No real-time monitoring: 88% of OT networks globally still struggle with detection and response, meaning breaches often go unnoticed for weeks.
IIoT Security Best Practices for Indian Manufacturers
A practical OT security India program does not require ripping out existing infrastructure. It requires a layered approach built around visibility, segmentation, and continuous monitoring — the same principles hIOTron applies when deploying hIOTron’s FactoryMetrics platform across automotive, electronics, and pharma plants.
1. Build a Complete Asset Inventory
You cannot protect what you cannot see. A working inventory should list every PLC, HMI, SCADA server, industrial PC, engineering workstation, switch, firewall, wireless access point, and IIoT sensor on the floor — including vendor-managed and remote-access devices that plant teams often forget to track.
2. Segment IT and OT Networks
Network segmentation is consistently cited as one of the single most effective controls for reducing manufacturing cyber risk. Separating production networks from administrative systems and externally accessible environments limits how far an attacker can move after an initial breach, containing damage to a single cell rather than the entire plant.
3. Run Regular Vulnerability Assessments
Scheduled Vulnerability Assessment and Penetration Testing (VAPT), along with disciplined patch management, helps identify exposed ports, outdated firmware, and misconfigured devices before an attacker does. For plants running older PLCs, virtual patching and compensating controls can reduce risk even when a device cannot be updated directly.
4. Enforce Strict Access Control
Every IIoT sensor, gateway, and remote-access session should require unique credentials, multi-factor authentication where feasible, and least-privilege permissions. Default passwords on sensors and edge devices remain one of the easiest entry points attackers exploit on Indian shop floors.
5. Monitor Continuously, Not Periodically
Real-time monitoring — ideally through a 24×7 Security Operations Center (SOC) — closes the detection gap that leaves most OT networks blind to active intrusions. Platforms like hIOTron’s FactoryMetrics combine edge computing with centralized analytics, giving plant IT teams a single dashboard to spot anomalous device behavior before it becomes a shutdown.
6. Prepare an Incident Response and Backup Plan
Secure, tested backups of PLC logic, HMI configurations, and production data reduce recovery time dramatically if ransomware does hit. A documented incident response plan — with clear roles for IT, OT, and plant leadership — turns a chaotic shutdown into a managed recovery measured in hours, not weeks.
Industry-Specific Considerations Across Indian Manufacturing
Security priorities shift depending on the industry. hIOTron works across automotive, aerospace, electronics, chemicals and pharmaceuticals, plastics and packaging, heavy engineering, and process manufacturing, and each vertical carries distinct exposure.
- Automotive: Just-in-time production and IATF 16949 compliance mean even short outages ripple through OEM supply chains.
- Pharma and chemicals: Regulatory bodies like CDSCO expect tamper-proof, auditable production data — a target attackers know is high-value.
- Electronics: Dense sensor networks and rapid product cycles widen the attack surface with every new device added.
- Heavy engineering and process manufacturing: Legacy PLCs running decades-old firmware are common, making network segmentation and compensating controls essential.
Building Security Into Your Industry 4.0 Roadmap
The mistake many Indian manufacturers make is treating security as a project to tackle after IIoT rollout, rather than a requirement baked into the deployment itself. As factories scale from pilot sensors to plant-wide Industry 4.0 implementation, security architecture should be designed alongside OEE monitoring, predictive maintenance, and quality control systems — not bolted on afterward. This is precisely why hIOTron builds segmentation-ready architecture and encrypted device communication into FactoryMetrics from day one, rather than treating it as an add-on module.
A Practical IIoT Security Checklist for Plant Managers
For plant managers who need to start somewhere without waiting for a full security overhaul, the following checklist mirrors what hIOTron recommends during early-stage Industry 4.0 implementation India projects. None of these steps require replacing existing machinery — they layer on top of what is already running on the floor.
- Map every connected device, including sensors added informally by maintenance teams outside official procurement.
- Change all default credentials on PLCs, HMIs, and IIoT gateways during the next scheduled maintenance window.
- Isolate the production VLAN from office networks and guest Wi-Fi with a properly configured firewall.
- Require contractors to use company-issued, scanned devices instead of personal laptops or USB drives on the shop floor.
- Schedule quarterly VAPT reviews for internet-facing OT assets, prioritizing devices with known exploited vulnerabilities.
- Set up automated alerts for unusual device behavior, such as a sensor suddenly communicating with an unfamiliar IP address.
- Test backup restoration at least twice a year, not just backup creation.
Aligning Security with India’s Regulatory and Compliance Landscape
Indian manufacturers exporting to global markets increasingly face compliance expectations that overlap directly with security hygiene. Automotive suppliers working toward IATF 16949 need auditable, tamper-resistant production records. Pharmaceutical plants under CDSCO and international GMP frameworks must demonstrate that batch data has not been altered — something unsegmented, poorly monitored networks cannot reliably guarantee. Building IIoT security India practices around asset visibility and continuous monitoring therefore serves two purposes at once: reducing breach risk and strengthening the audit trail regulators and OEM customers increasingly demand.
As more Indian plants pursue Make in India-linked incentives tied to digital manufacturing readiness, security posture is quietly becoming a competitiveness factor, not just a defensive one. Global OEMs now routinely include cybersecurity questionnaires in supplier onboarding, and plants that can demonstrate segmented networks, monitored IIoT fleets, and documented incident response plans have a real edge in winning that business.
Frequently Asked Questions
What is industrial IoT security and why does it matter for Indian factories?
Industrial IoT security protects the sensors, PLCs, gateways, and networks that connect factory equipment from cyberattacks. It matters in India because manufacturing has become the most targeted sector for ransomware, and a single breach can halt production lines for days.
How is OT security different from regular IT security?
OT security protects physical industrial systems like PLCs and SCADA that control machinery, where downtime has physical and safety consequences. IT security protects data and computing systems. OT environments often run legacy devices that cannot be patched the same way IT systems can.
What are the biggest IIoT cybersecurity risks for manufacturing plants in India?
The biggest risks include flat IT-OT networks, unmanaged sensors and devices, default credentials on IIoT hardware, contractor laptops and USB drives, and a lack of real-time monitoring that lets intrusions go undetected for weeks.
How much does industrial IoT security implementation cost for an Indian manufacturer?
Costs vary by plant size and existing infrastructure, but layered programs combining network segmentation, VAPT, and continuous monitoring are typically far less expensive than a single ransomware-driven shutdown, which can cost lakhs to crores in lost production and recovery.
Can a secure IIoT platform also improve productivity, not just protect against attacks?
Yes. Platforms like FactoryMetrics are built with segmentation and encrypted communication by default, so security controls run alongside OEE monitoring, predictive maintenance, and real-time analytics without slowing down production data flow.
Secure Your Smart Factory Journey with hIOTron
Industrial IoT security India is not a one-time project — it is an ongoing discipline that must scale alongside your plant’s digital transformation. hIOTron’s FactoryMetrics platform combines plug-and-play IoT hardware, AI-driven analytics, and no-code workflow automation with security architecture designed for Indian manufacturing environments, from automotive to pharma. Explore hIOTron’s Industry 4.0 solutions to see how a secure, connected factory floor can protect production while driving OEE, quality, and energy gains.